
Surprisingly Useful AI Article Enhancements
Microsoft has introduced new FIDO2 provisioning APIs for its Entra ID platform, aiming to strengthen phishing-resistant security measures for enterprises and governments. This development is part of a continued partnership with Yubico, which has worked with Microsoft for over a decade to enhance the security of Microsoft solutions against phishing attacks – especially against users with business laptops.
Recognising the growing importance of multi-factor authentication (MFA), Microsoft recently mandated that all Azure users implement MFA, a move intended to provide stronger protection against phishing. Yubico, a long-time collaborator, supports this mandate and encourages organisations to adopt modern MFA solutions beyond Azure, advocating for phishing-resistant methods like the YubiKey across all user applications.
Srujan Talakokkula, Managing Director for ANZ Commercial at Trend Micro, highlighted the significance of this advancement: “We are not just adapting to an Ai-driven world; we are creating it. Our goal is to ensure that any team can securely innovate without increasing risk. When implemented correctly, new technology should enhance business resilience, not compromise it. Just as we led the way with cloud security, we are now pioneering Ai for security and security for Ai.”
Expanding Phishing-Resistant Security
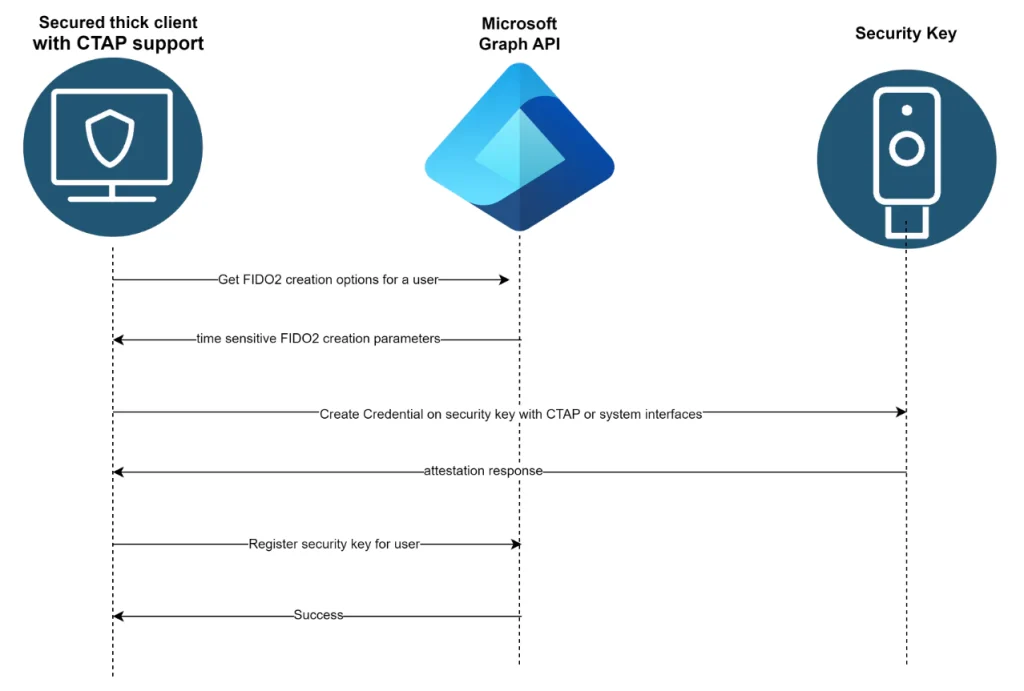
With the introduction of the Entra ID FIDO2 provisioning APIs, organisations now have the flexibility to develop or use alternative administrator-led provisioning clients. These clients support the setup of hardware security keys, such as the YubiKey, without requiring users to register their own security keys—a process that previously often necessitated the use of phishable methods like Temporary Access Passes.
This capability is particularly beneficial for diverse, multinational entities and government agencies that require high levels of security. With the new APIs, users can now be onboarded or recover their accounts without relying on potentially vulnerable authentication methods.
Natee Pretikul, Principal Product Management Lead at Microsoft Security, commented on the collaboration: “Phishing-resistant MFA is essential for maintaining a robust cybersecurity practice. Our integration of the FIDO2 Provisioning API with Yubico’s solutions allows our enterprise customers to implement YubiKeys quickly, enhancing protection for their employees more efficiently. Together, we are helping customers safeguard their digital identities and protect their data against evolving threats.”
Integrating YubiKeys Across the Microsoft Ecosystem
YubiKeys offer a strong line of defence against account takeovers by providing secure two-factor, multi-factor, and passwordless authentication. While MFA is widely regarded as a critical security measure, not all MFA methods are equally secure. Traditional methods like passwords are easily compromised, and mobile-based authentication methods—such as SMS, OTP codes, and push notifications—are susceptible to phishing, malware, SIM swaps, and attacks in the middle (AiTM).
This is especially relevant for organisations using Microsoft environments, where integration of services like Azure, Microsoft 365, and Dynamics 365 means that a single account takeover could have significant consequences. The YubiKey addresses these risks by offering a bridge from legacy authentication methods to modern, secure options. It supports on-premises Smart Card deployments, cloud app authentication through FIDO2, and integrates seamlessly with devices like the Surface Pro 10 for Business.
Alex Yeh, CEO at GMI Cloud, an Ai technology partner with Trend Micro, praised the integration: “We have not seen anyone introduce security capabilities at this level for Ai technology. The ability to use the same Ai security rules and platform to manage customers’ Ai data tools across any environment is invaluable.”
Preparing for the Future
As cyber threats continue to evolve, Microsoft’s partnership with Yubico ensures that security measures remain ahead of potential risks. Organisations are encouraged to prepare for the Azure MFA mandate by reviewing Microsoft’s guidance and identifying impacted users. Beyond the mandate, enforcing phishing-resistant MFA for all users and applications is recommended, using built-in Authentication Strength features or custom solutions.
Organisations looking to strengthen their security posture can begin by exploring how to leverage the Microsoft FIDO2 registration APIs. These tools support high-assurance onboarding and account recovery processes, ensuring that even in the face of evolving threats, enterprises can maintain secure operations.
For more details on the Microsoft MFA Mandate, the new Entra ID FIDO2 provisioning APIs, and how to implement YubiKeys in your business, Microsoft and Yubico provide resources and guidance to help organisations take the next step in becoming phishing-resistant.
Last Updated on August 9, 2024 by Nick Ross


